
Why AI Agents Need Task History and Audit Logs: A Guide to Accountability
An Agent audit log should not be a raw developer trace. What users truly need is a readable cause-and-effect chain: who initiated it, how the Agent understands it, what was called, who approved it, what results were produced, and whether it can be revoked.
When the AI generates only one piece of text, the history record mainly helps users retrieve the content. When AI agents can update CRM, modify files, call apis, send messages and even trigger payments, "history" becomes evidence of responsibility. Without a task history, users cannot answer the most fundamental question: What exactly happened just now?
01 Audit the causal chain, not every token
A useful Agent audit record should be understandable to non-developers: who proposed the goal, what key decisions the system made, which tools were called, which steps were manually approved, what changes occurred in the external state, and finally how the results were verified.
02 Separate user history, operational logs, and technical traces
User history is oriented towards business users, emphasizing tasks and results. The operational and compliance log is for administrators, focusing on identity, permissions, approvals, and anomalies. Technical traces serve engineering teams and include details such as model requests, tool latency, and error stacks. Stuffing all three types of information into one page will not only be difficult to read but also leak sensitive information.
03 Preserve six kinds of evidence for every task
- Initiator and Time: Who initiated it at what time and in which workspace.
- Objectives and Inputs: The user's original objectives, as well as the constraints that were later supplemented or modified.
- Planning and Key Decisions: Which steps did the Agent choose and why did they switch paths?
- Tools and Permissions: What systems were called, what resources were read and written, and what authorizations were used.
- Manual approval: approver, specific parameters for approval, scope of approval and time.
- Results and verification: What was actually changed, whether it was successful, whether it was rolled back, and subsequent status.
04 Organize logs around the task timeline
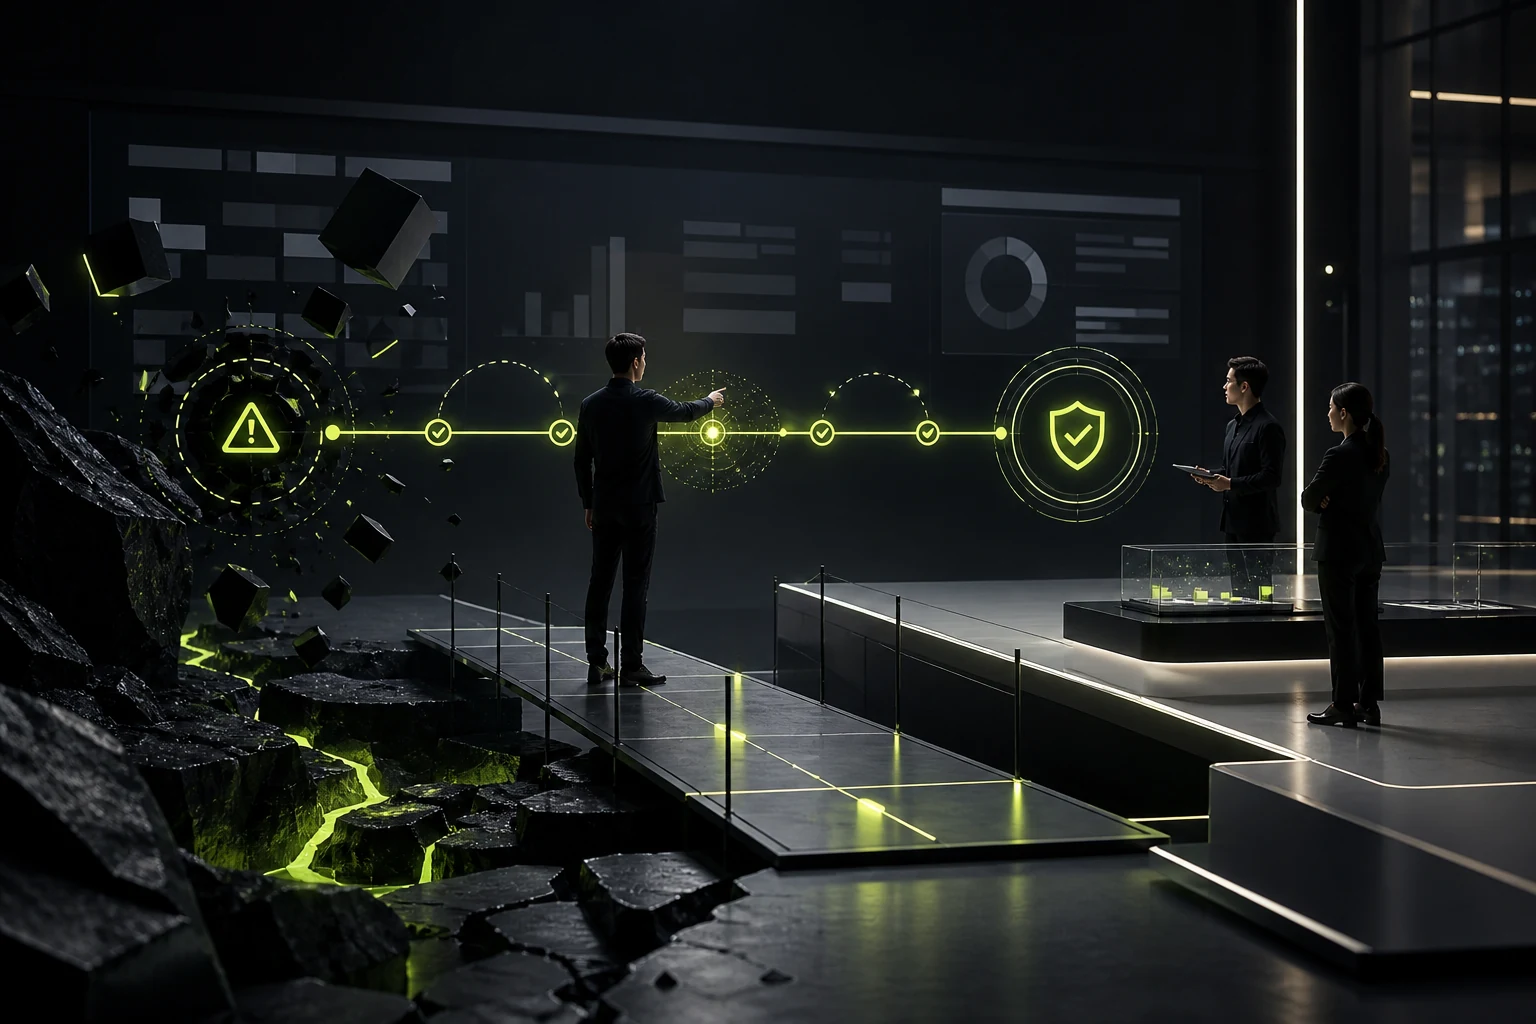
Rather than arranging 200 records by system events, a more suitable timeline for users is: understanding the task → collecting information → proposing an operation → waiting for approval → execution → verification. Each stage can be folded, with key summaries displayed by default. When needed, the original request, API parameters, and evidence can be expanded.
05 Preserve what users saw when they approved an action
It is not enough to only record "User clicks to approve". A truly accountable approval should preserve the action object, scope, amount, recipient or other key parameters displayed at that time. If the Agent modifies the parameters after approval, the system should request confirmation again instead of following the old approval.
06 Record external effects separately from tool calls
The successful invocation of a tool does not necessarily mean the success of the business outcome. For example, the API returns 200, but the email is actually rejected; The CRM update was successful, but the field values do not comply with the rules. The log should simultaneously record "execution actions" and "verification results" to prevent the system from misjudging the completion of a call as the completion of a task.
07 Keep sensitive information auditable without exposing it indefinitely
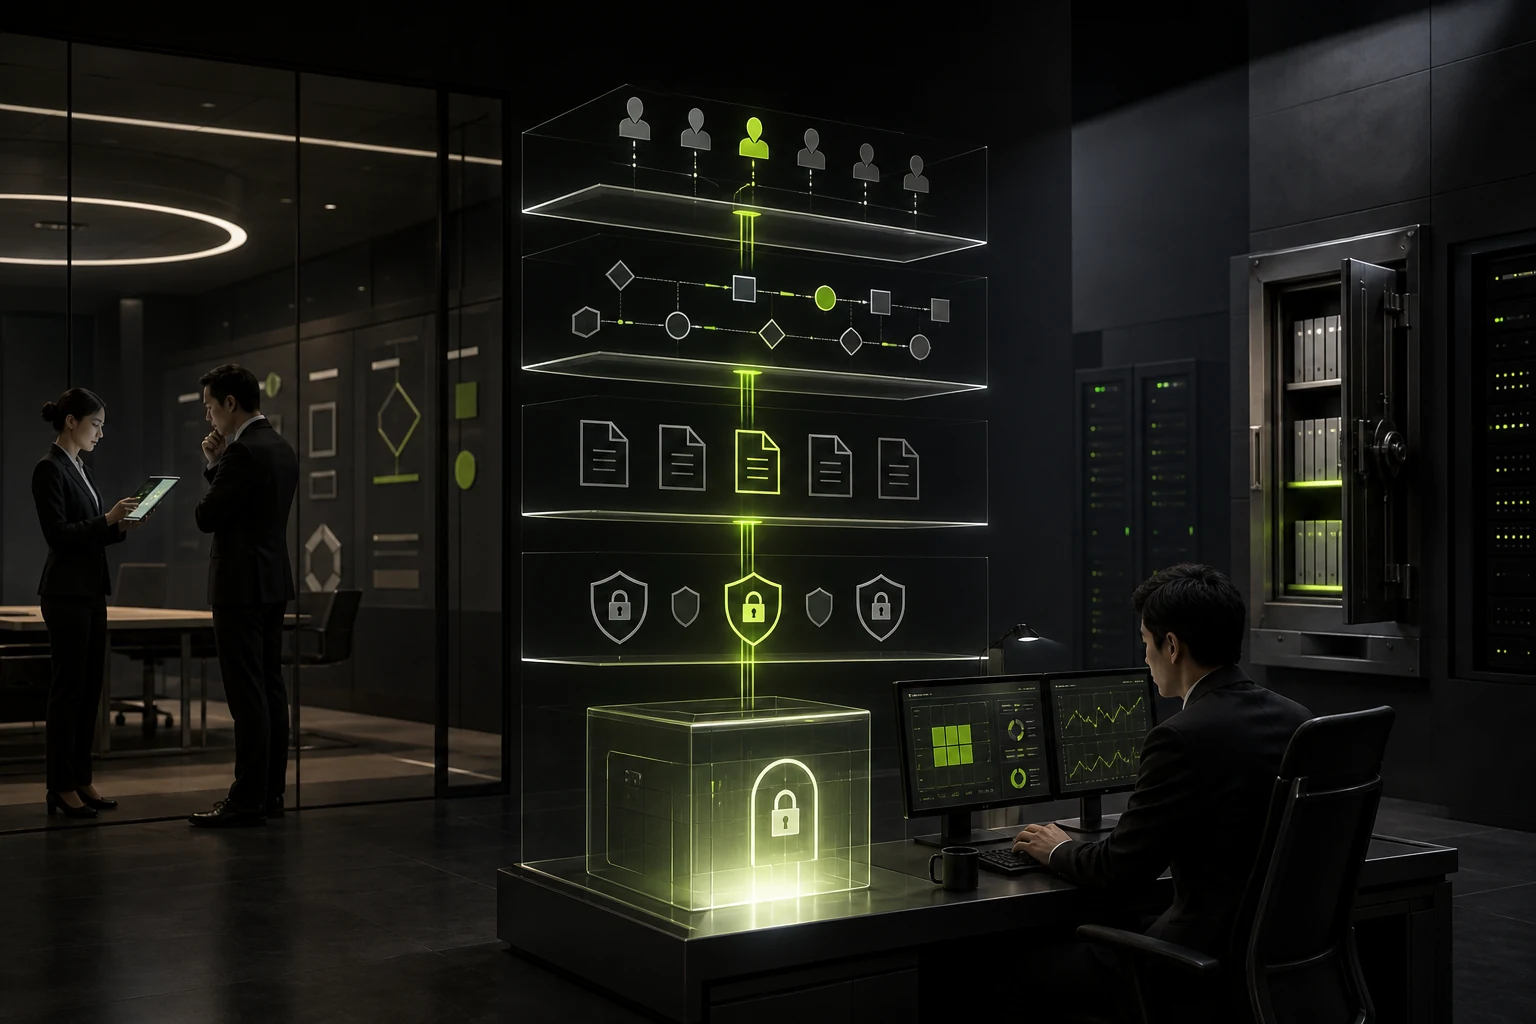
Audits require sufficient evidence and may also include customer data, keys, prompts or restricted documents. The interface should be desensitized and access controlled based on roles. tokens, keys, and complete file contents in technical logs should usually not be directly displayed to ordinary administrators. The retention period should also be determined by the organization's risk and compliance requirements.
08 Support revocation and incident investigation
If the action is reversible, the task history should directly provide a recovery entry and clearly show what the recovery will affect. For actions that cannot be automatically revoked, an impact list should also be retained to assist in manual repair. When a security incident occurs, administrators should be able to quickly filter by Agent identity, tool, user, time and resource.
09 Treat Agent history as a first-class product page
Don't hide it in the "Developer Settings". For a truly action-oriented Agent, task history, approval, and exceptions themselves are the user trust interface. The easier it is for users to review an action, the more willing they are to entrust the next task to the system.
10 Define consistent event semantics across tools
When the Agent connects to dozens of systems, the original log names will be very confusing: tool_call, API request, function result, workflow step. The product layer should be abstracted into stable event types, such as "read resources, generate proposals, request approval, execute changes, verify results, undo operations, and deny permissions". This way, administrators can filter across tools, which is also convenient for subsequent compliance and alerts.
The event should also retain the object ID, the summary of the status before and after the action, the Agent identity, the initiating user, the approver and the associated task. For batch operations, it is best that the log has both task-level summaries and can be expanded to individual objects.
11 Separate readable summaries from raw evidence
Ordinary business users need 30 seconds to understand what is happening. The security team may need complete requests, responses, and timestamps. The natural language timeline can be displayed by default, and Evidence/Raw details can be provided for authorized roles at the same time. This way, it not only avoids overwhelming users with technical noise but also prevents the loss of audit evidence due to the pursuit of simplicity.
Frequently Asked Questions
What are the differences between AI Agent audit logs and ordinary operational logs?
The Agent needs to record additional aspects such as target understanding, planning, model decision-making, tool invocation, manual approval, and external effects in order to restore the complete causal chain.
Is it necessary to save the complete prompt and model output?
Technical troubleshooting may be necessary, but it should not be displayed to all users by default. Sensitive data, retention periods and access rights should also be taken into consideration.
Why do approval records need to keep specific parameters?
Because the responsibility meanings of "approving an action" and "approving a specific recipient, amount, or document" are completely different.
Can logs help prevent prompt injection?
Logs themselves cannot prevent attacks, but they can help detect abnormal tool calls, track the scope of impact, investigate the root cause, and improve permission policies.
How long should the Agent history be retained?
There is no uniform answer. It should be determined based on data sensitivity, business risk, compliance and incident investigation needs, and a hierarchical retention and deletion strategy should be set.
| Related Service | Learn More |
|---|---|
| UI/UX Design Services | View Service Details |
| Project Consultation | Contact JVDS Design Studio |
| Design and Website Development Articles | Read More Related Articles |
 Link copied








