
How to design a Cookie pop-up window on an enterprise's corporate website? "Acceptance" is conspicuous while "refusal" is hidden, which not only damages trust but may also bring compliance risks
The Cookie pop-up window is not simply "put an accept button" and it's done. When targeting markets such as the UK and the EU, non-essential tracking usually requires genuine selection. In terms of experience, acceptance and rejection should not be designed as a visual inducement either.
01 Cookie Banner is first a selection interface, not a marketing position
When many enterprises build overseas corporate websites, they treat the Cookie pop-up as a necessary compliance component: a black banner at the bottom, a long legal document on the left, a prominent "Accept All" on the right, and hiding the rejection in "Settings" beside it. The page seems to have completed the task, but users do not receive truly equivalent choices.
The applicable rules vary from country to country and region to region. This article is not a legal opinion, but the public guidance from the UK's ICO and the French CNIL both provide very clear design directions: for non-essential tracking, users should be able to make real choices rather than pushing people towards acceptance through visual or interaction costs.
02 Accept and reject should not be "one-click vs. three-tier Settings"
The CNIL's public Q&A clearly states that refusing cookies should be as easy as accepting them, and for example, it suggests providing "Tout accepter/Tout refuser" at the same level. The enforcement materials of the UK ICO against Cookie banners also pointed out that the absence of an equally prominent "Reject All" option may not lead to meaningful consent.
Therefore, a common but high-risk design is that the main button "Accept All" uses high-contrast fill, and the rejection can only be done by first entering the Settings, then closing each item one by one, and finally saving. It may increase the acceptance rate in terms of conversion, but it artificially makes the choice cost asymmetrical.
03 Non-essential cookies should not secretly start working before consent is given
The public enforcement statement of the ICO also emphasizes that non-essential advertising cookies should not be placed before the user's valid consent. If the user chooses to reject, these trackers should not continue to be placed either. For the design team, this means that the Cookie Banner is not a pure UI project; it must be synchronized with the actual script loading logic.
The presence of "Reject All" in the design draft does not mean that the website truly respects rejection. Development requires managing scripts such as analysis, advertising, and personalization by type, and ensuring that user choices can truly affect whether they load or not. Essential cookies and non-essential cookies should also be clearly distinguished in the text and Settings.
04 What should be clearly stated in the first-level pop-up window and what should not be
The first layer of information does not need to include the entire privacy policy. The user needs to quickly know: why this pop-up window appears, which major types of cookies are used, which ones are unnecessary, what impact his choices will have, and where further Settings can be made.
The copy should be specific. Do not use expressions like "To provide the best experience, we use cookies" that only offer benefits and have no actual purpose. A more transparent approach is to describe different purposes such as "for basic website functions, visit statistics, and marketing measurement", and link detailed explanations to the Cookie policy or preference Settings.
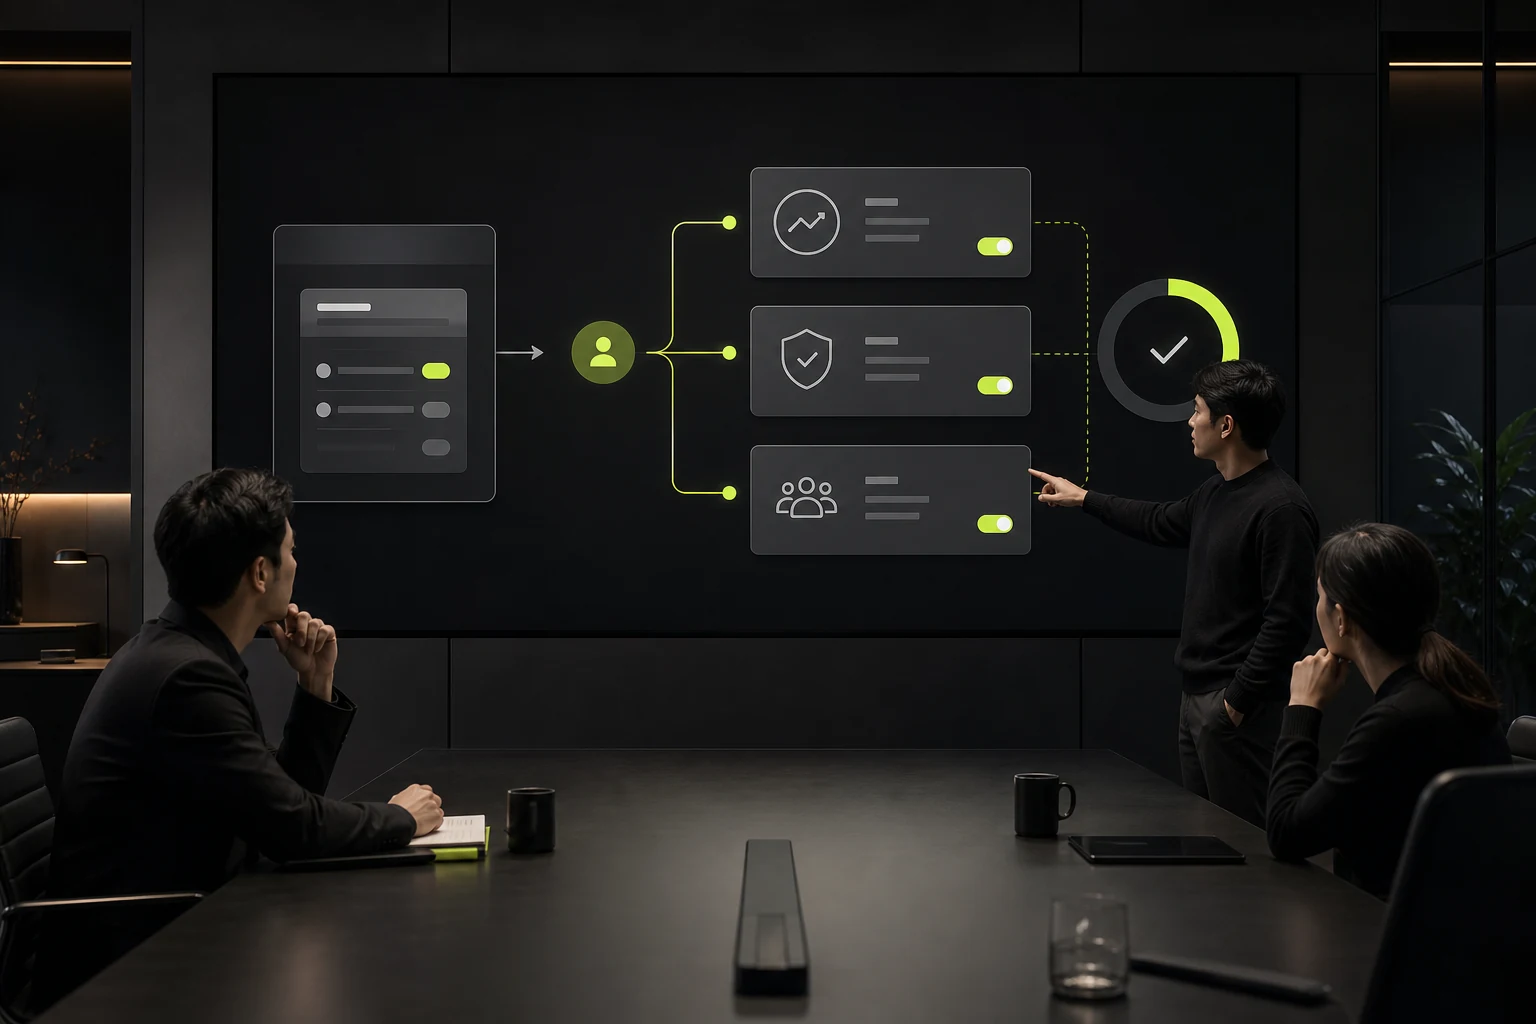
05 The secondary Settings should be organized by "purpose" rather than allowing users to view the technical checklist
Ordinary users usually cannot determine what Cookie names such as _ga, IDE, and fr mean. The Settings panel is more suitable for grouping by purposes such as "necessary", "Statistics", "Personalization", "advertising/marketing", etc., and then allows users to further view specific services and retention periods.
Necessary classes can clearly explain why they cannot be closed. For other categories, clear switches or checkboxes should be used. Do not default to enabling them and then use vague text to induce users to retain. The Settings panel should also have a clear "Save Selection", and ensure that closing, returning, and keyboard operations are all normal.
06 Users should be able to modify later instead of "select once and it will take effect permanently"
The public guidance of CNIL suggests that users can withdraw their consent at any time, for example, through the Cookie Settings entry in the footer. It also suggests remembering to agree or reject for a period of time to avoid repeated pop-up harassment.
From the perspective of experience, this is extremely important. If the Cookie Banner only appears during the first visit and the user cannot find the Settings later, they will lose control. The corporate website can provide "Cookie Settings" near the privacy policy, at the bottom of the page, or in a fixed privacy entry, allowing users to reopen the management panel.
07 Do not use dark mode for the sake of acceptance rate
Common dark modes include: making the reject button close to the background color, closing the pop-up window equals default acceptance, using "Continue browsing to agree" to imply passive acceptance, hiding "only necessary" very deeply, or reopening the pop-up window each time the user visits until they accept.
These practices may make the statistics more complete in the short term, but they will directly damage users' trust. For enterprises that hope to establish a long-term brand overseas, a fair and clear privacy interface itself is also part of professionalism.
08 Conclusion: Consider Cookie selection as a brand trust test
A mature Cookie Banner should achieve the following: clear purpose, easy to accept and reject, non-essential scripts respect choices, Settings can be reopened, and visually not deliberately induce.
The specific legal requirements should be confirmed by professional legal or privacy personnel based on the enterprise's service region, tracking technology and data processing methods. However, the design team can at least adhere to one principle first: the choices seen by users should be genuine, and the interaction cost of each option should be reasonable.
Frequently Asked Questions
Does a corporate website necessarily need a Cookie pop-up window?
Not necessarily. It depends on the Cookie/ tracker used, the service region and applicable laws. The situation where only strictly necessary cookies are used may differ from the requirements for using AD tracking.
Can "closing a pop-up window" equal consent?
It should not be designed in this way under many agreed frameworks. Take the guidance of CNIL as an example. Except for the explicit acceptance action, actions such as closing should not be regarded as consent.
Must the reject button be exactly the same as the accept button?
Different jurisdictions have different expressions, but the core point is that rejection cannot be significantly more difficult than acceptance. The CNIL clearly requires that rejection should be equally easy.
Where should the Cookie Settings entry be placed?
A common practice is to provide it for a long time in the footer, privacy center or fixed privacy entry so that users can modify and select it later.
Is the use of the Cookie Banner tool definitely compliant?
Not necessarily. Components are merely interfaces. It is also necessary to check whether the actual script is loaded before agreement, whether it stops after rejection, and whether the policy content is consistent with the actual processing.
| Related Service | Learn More |
|---|---|
| Corporate Website Design Services | View Service Details |
| Project Consultation | Contact JVDS Design Studio |
| Design and Website Development Articles | Read More Related Articles |
 Link copied








