
After a corporate website launches, the team may receive dozens of daily submissions advertising SEO, proposing vague partnerships, or containing garbled text. The first reaction is often to add a difficult CAPTCHA. Bots decline, but genuine prospects also abandon the form.
The goal of form protection is not to block every anomaly at the perimeter. It is to raise the cost of automated abuse without adding obvious friction for legitimate users.
01 Identify Where Spam Submissions Come From
Review submission times, field content, IP addresses, User-Agent values, source pages, and request frequency to distinguish simple scripts, manual bulk submissions, direct API calls, and automation that bypasses frontend checks.
If validation or endpoint hiding exists only in the frontend, bots can call the backend directly. Repeat every critical check on the server.
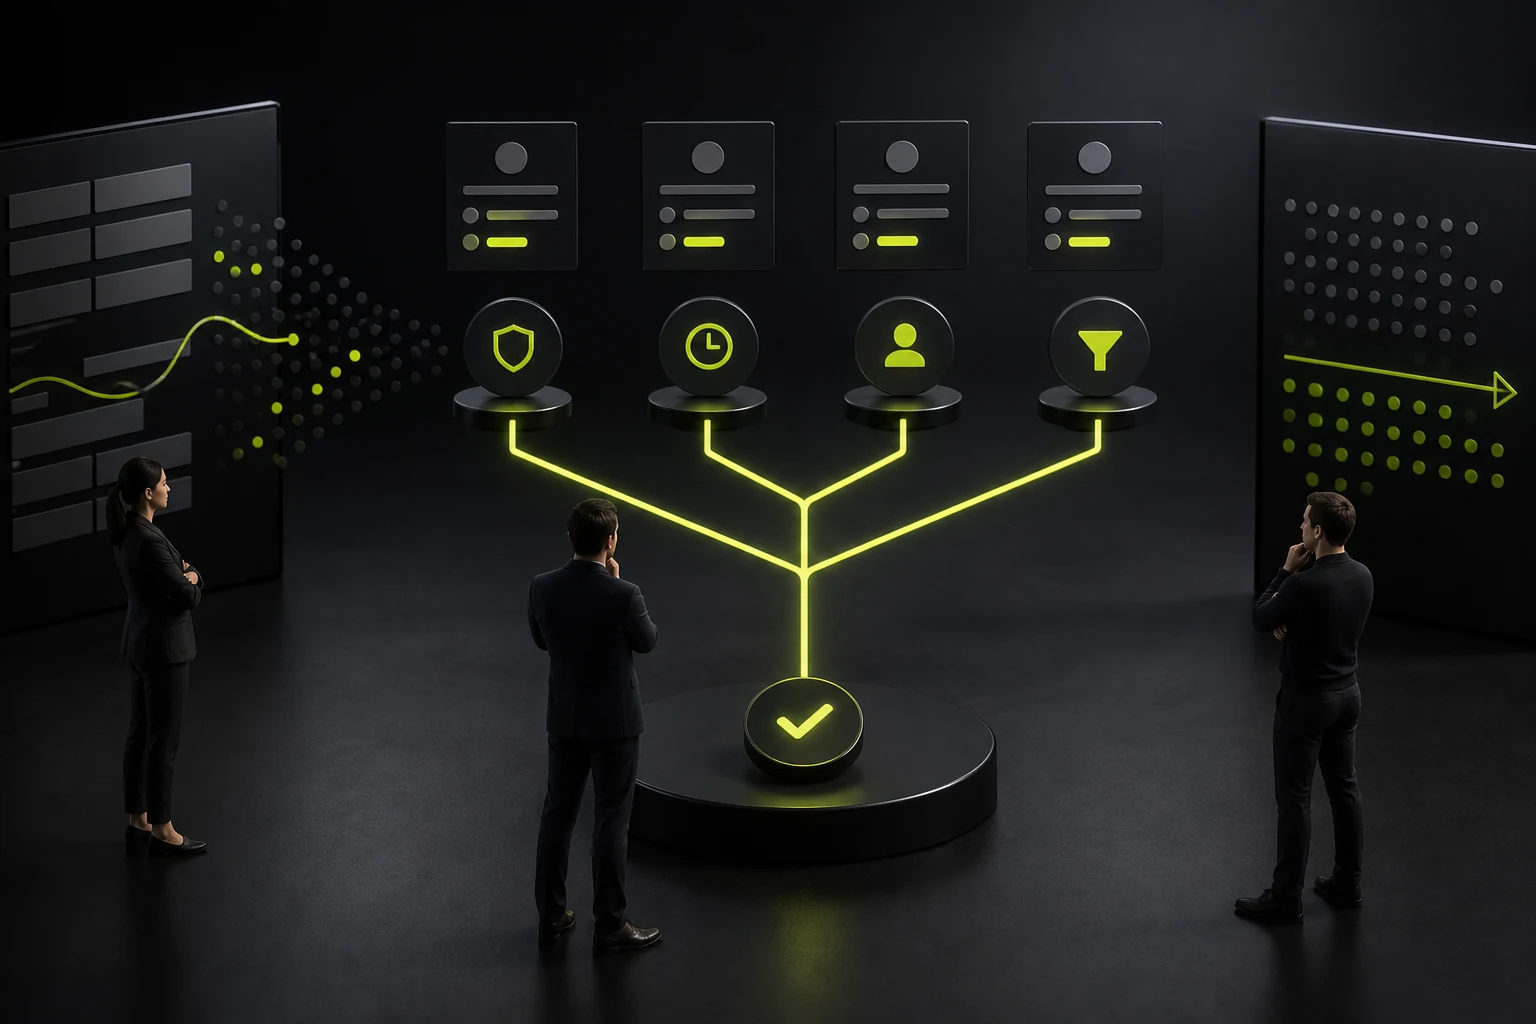
02 Layer Low-Friction Measures First
Honeypot fields, minimum completion time, CSRF protection, field-length limits, and server-side format validation are nearly invisible to legitimate users but filter many basic scripts.
A correctly formatted email address or phone number is not proof of genuine content. Also inspect repeated text, link count, unusual characters, and bursts of frequent submissions.
How to Choose Common Anti-Spam Measures
| Measure | Best For | Considerations |
|---|---|---|
| Honeypot field | Bots that automatically complete every field | Hide it from users and validate it on the server |
| Rate limiting | High-frequency requests from one source | Combine IP, session, and account signals to avoid blocking shared networks |
| Behavioral CAPTCHA | Secondary verification for suspicious requests | Trigger it only when risk rises to reduce friction |
| Content rules | Repeated text, excessive links, and keyword spam | Tune continuously to avoid misclassifying legitimate inquiries |
| Email or SMS confirmation | High-value appointments or registrations | Adds cost and abandonment; not suitable for every form |
| WAF or risk service | Large-scale attacks and known malicious sources | Monitor rules, privacy implications, and third-party cost |
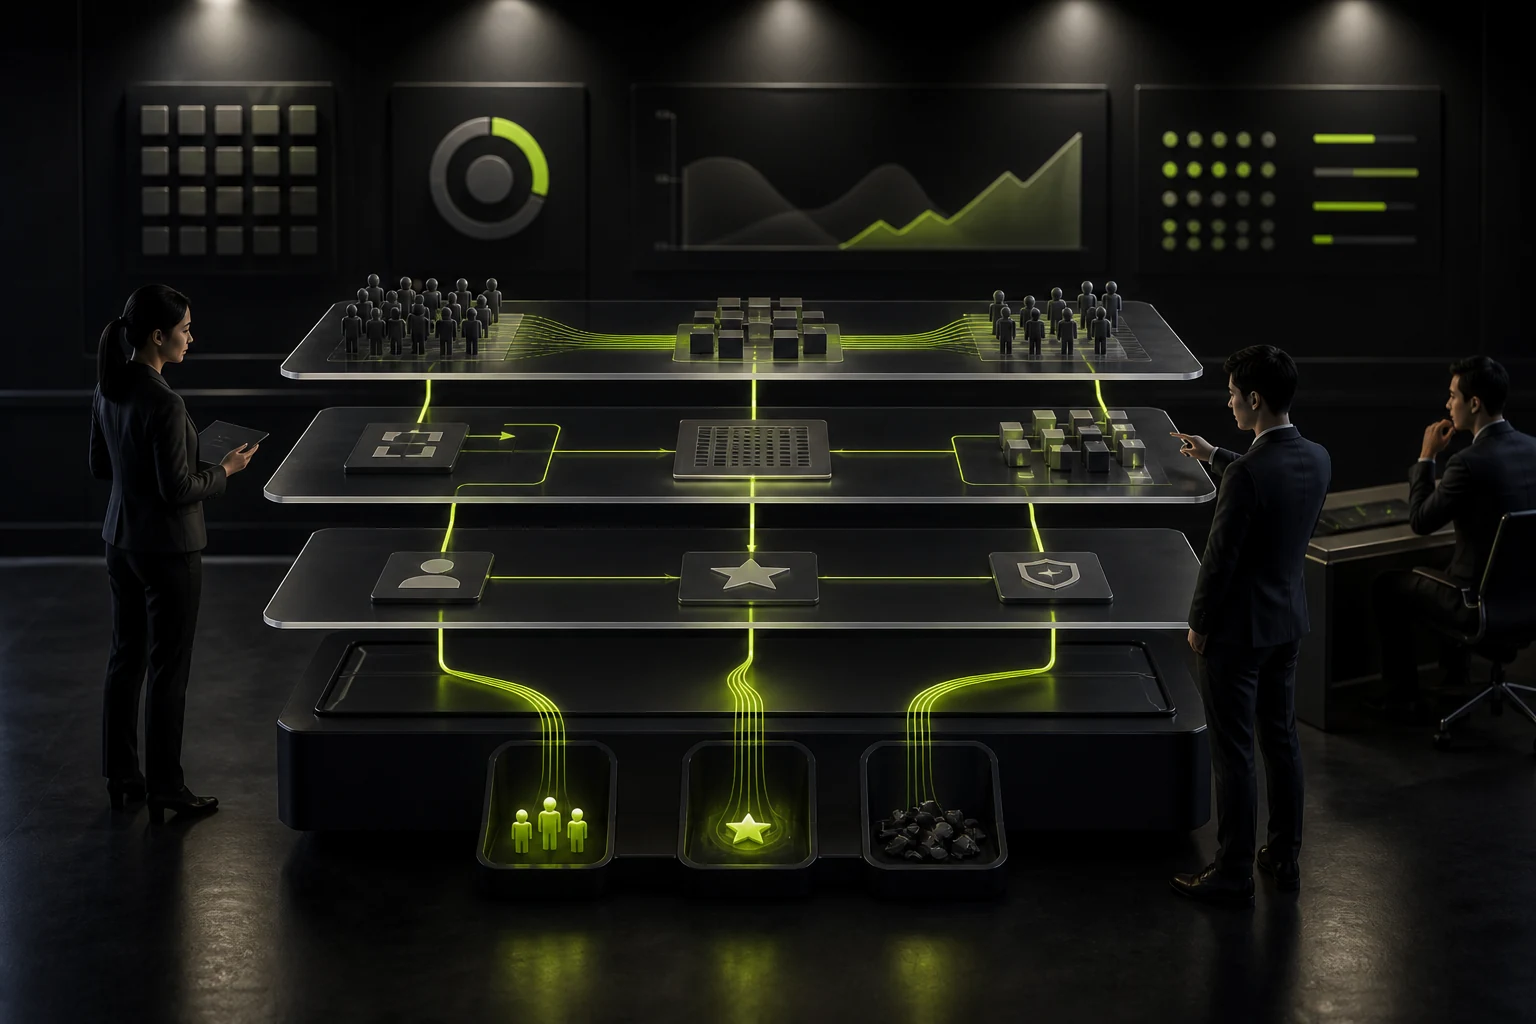
03 Set Rate Limits According to Business Value
A standard contact form can limit repeated submissions over a short period. Login, verification-code, and password-reset endpoints need stricter limits across multiple dimensions.
Blocking only by IP can harm users behind corporate networks or mobile carriers. Combine cookies, device characteristics, sessions, and behavior where appropriate, but do not collect more data than necessary.
04 Use CAPTCHA as an Escalation, Not the First Gate
Showing a challenge only when a risk score becomes unusual is more reasonable than making every visitor solve a puzzle. CAPTCHA does not replace server-side validation and may still be bypassed through human-solving services or automation.
Mobile users, keyboard users, and people using assistive technology must also be able to complete verification. Do not treat an accessibility barrier as an acceptable security cost.
05 Log Blocks and Provide a Recovery Path
Record which rule fired, the time, request identifier, and result so the team can identify overly aggressive controls. Do not retain unnecessary sensitive form content in logs.
If a high-value lead is blocked, provide a backup phone number, email address, or retry instruction instead of only “Submission failed.”
06 Remove Attack Surfaces and Update Dependencies
Deprecated endpoints, old forms, test pages, and outdated plugins frequently become entry points. Delete unused endpoints, update frameworks and dependencies, and limit administrative access.
After launch, monitor spam rate, false-positive rate, completion rate, and the distribution of triggered rules. Looking only at lower spam volume may hide a decline in genuine leads.
Frequently Asked Questions
Will reCAPTCHA stop all spam submissions?
No. CAPTCHA is one layer and should work with server-side validation, rate limits, and logs.
Does hiding the form endpoint help?
It is not a security control. Bots can discover the endpoint by crawling or inspecting network requests, so the backend must validate independently.
Why can bots bypass required-field validation?
They can call the submission endpoint directly without executing the page's JavaScript.
Is blocking IP addresses the most effective control?
It works against fixed sources but proxies bypass it easily, and it can block shared networks. Combine it with other signals.
How can we tell whether CAPTCHA hurts conversion?
Compare form starts, completions, errors, valid leads, and mobile performance before and after activation.
| Service | View |
|---|---|
| Website development services | View service details |
| Project inquiry | Contact JVDS |
| Design and website articles | View service details |
 Link copied








