
To what extent can AI agents perform automatically? Truly high-risk actions must be designed with "confirmation, preview and revocation".
If an email is generated incorrectly, it can be rewritten. When AI automatically sends emails to customers, deletes databases or submits payments, the cost of errors is completely different. Agent UX cannot merely add a "Run" button. Instead, it is necessary to decide when to execute automatically and when it must be confirmed first based on the consequences.
01 Treat "suggestion" and "Execution" as two different permission levels
Traditional Copilot mainly offers suggestions and users complete the actions themselves. When the Agent starts to invoke the tool on behalf of the user, the product responsibility changes accordingly.
The interface should clearly distinguish between "AI suggests you do this" and "AI will actually execute". The buttons, status and language should not mislead users into thinking they are just previews.
02 Risk classification is more available than "All actions confirmed"
If AI pops up confirmation every time it creates an internal draft, the value of automation will drop rapidly. If the transfer and mass email sending are also completely automatic, the risk is too high.
It can be classified by reversibility, amount, external influence, data sensitivity and scope. Low-risk automatic execution, medium-risk batch confirmation, and high-risk item-by-item approval.
03 Before confirmation, a preview of the result should be displayed instead of just asking "Is it allowed?"
Microsoft HAX's Feedforward model emphasizes explaining the consequences before high-risk or hard-to-undo actions. The Agent confirmation page should show what will be modified, to whom it will be sent, and how many objects are involved.
"Allow AI to perform 8 operations?" " It is far less effective in judging than listing "sending emails to 3 customers, updating 4 CRMS, and creating 1 task".
04 Allows users to modify the plan before execution
The Agent plan consists of 10 steps, among which step 7 is inappropriate. Users should not be able to only "approve all" or "cancel all". It is allowed to delete a certain step, modify parameters, pause to a certain step and then confirm.
This editable plan is more effective in establishing a sense of control than hiding all Agent behaviors in the background.
05 Batch approval should clearly define the scope and common rules
If the 100 actions are essentially the same, for example, "Create drafts for all unreplied customers", users can be allowed to confirm the rules and execute them in batches.
However, once the data and consequences of each object are different, sampling preview, anomaly alerts or item-by-item approval are required. Efficiency should not come at the cost of invisible differences.
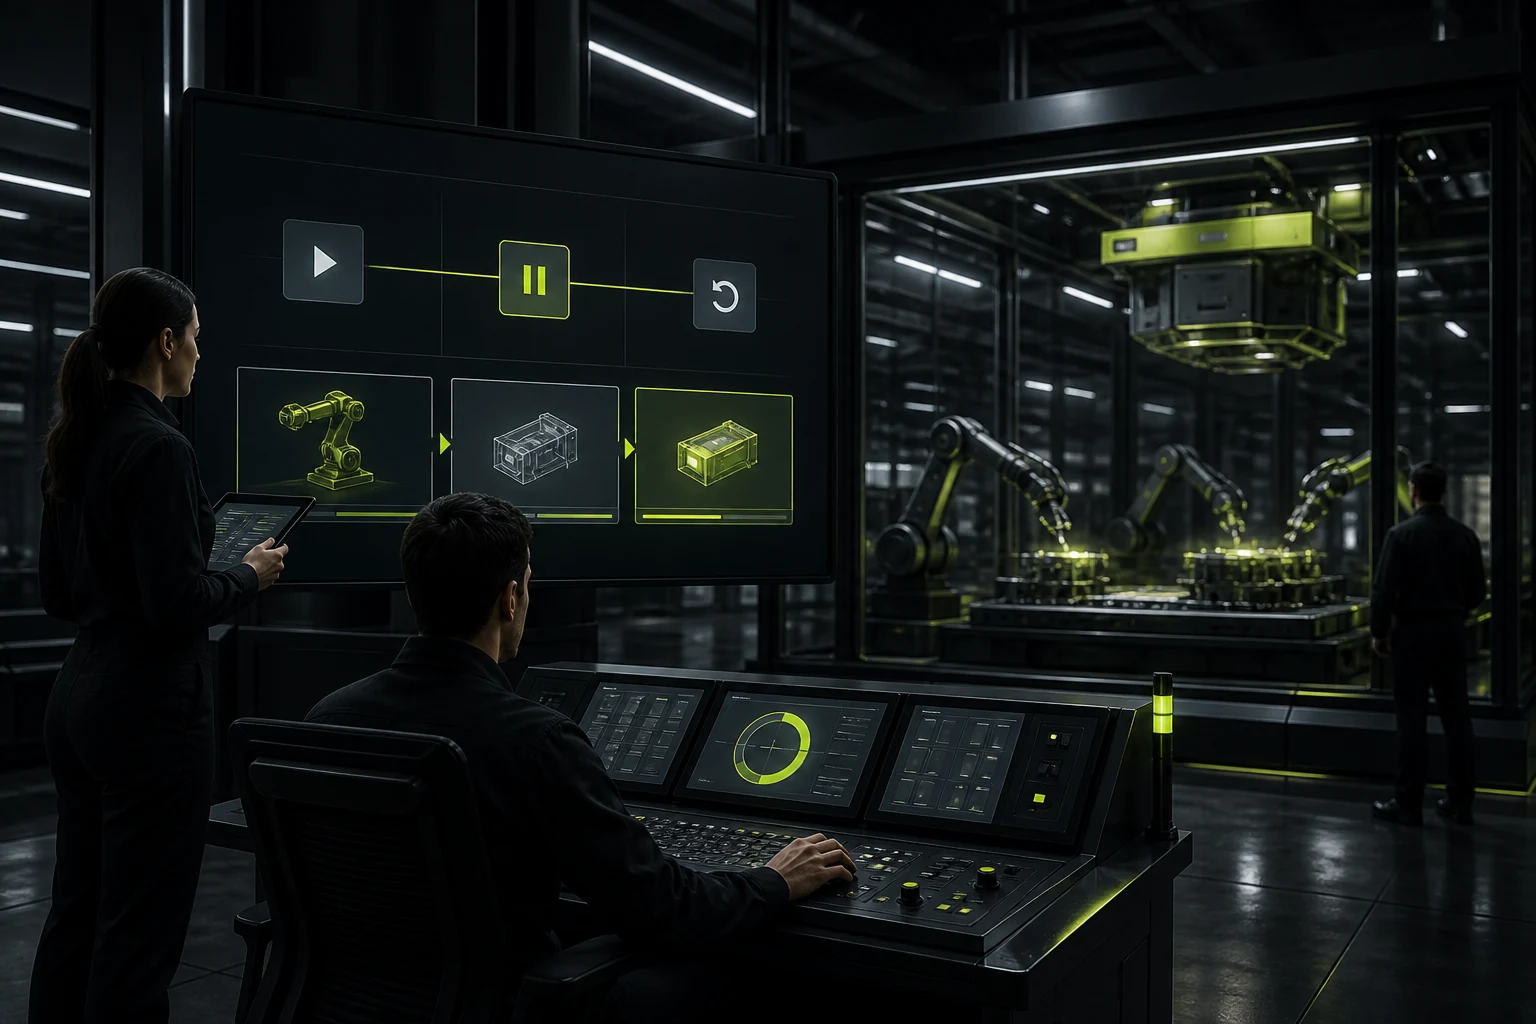
06 Pause should be supported during execution, and undo should be supported as much as possible after execution
Long tasks are not about clicking and waiting to end. The user needs to see the current progress, which steps have been completed, and whether it can still be stopped.
Reversible actions should be recorded as Undo or rolled back as much as possible. For irreversible operations, the confirmation intensity should be increased even more in advance.
07 The Agent must leave a traceable record of actions
NIST's generative AI risk framework emphasizes governance, measurement, and risk management. In the enterprise Agent scenario, there should be audit records for who initiated, what the AI did, what the user approved, and what the tool returned.
This is used both for security and compliance, and can also quickly rebuild the process when errors occur.
08 The best Agent automation is not "completely unmanned", but rather placing people at the most valuable decision-making points
Human-in-the-loop is not a fallback for failure, but a system design. Machines are good at repetitive execution, while humans are good at handling goals, exceptions, risks and responsibilities.
Only when the approval point is precisely located at a high-risk and high-uncertainty node can the Agent both enhance efficiency and prevent users from losing control.
09 High-risk agents can adopt the "plan - approve - execute" three-stage approach
The user first sees the plan drafted by the AI, confirms the goals and tools; Re-approve the key steps; Check the result after execution. Compared with a single command directly running in a black box, this structure makes responsibilities and changes clearer.
Not every task requires a complete three-part format, but it is very suitable when it comes to external sending, data modification and payment.
10 Default permissions should follow the principle of least necessity
If the Agent only needs to read the calendar, it should not be granted the default permissions to send emails, delete events and access all Drives. The larger the authorization scope of the connector, the more difficult it is for users to assess the risks.
The product can request additional capabilities when a certain action is needed and explain "why it is needed". This is both a security policy and a trust experience.
11 The execution result of the Agent should distinguish between "successful submission" and "actual completion".
Returning "accepted" when calling an external system does not mean that the order has been processed. The interface should track asynchronous results to prevent the situation where the AI says "completed" but external tasks are still queuing.
For users, the state semantics must be consistent with real-world consequences.
Frequently Asked Questions
Does an AI Agent need user confirmation every time it executes?
No need. Actions should be classified according to risk, reversibility and scope of impact. Low-risk actions can be more automated.
What is the most important thing to display on the confirmation page?
Specific actions, objects, scopes and irreversible consequences, rather than just showing a "allow/reject".
Can the Agent execute first and then Undo?
Reversible low-risk tasks are acceptable, but high-risk irreversible tasks should be confirmed before execution.
Is batch approval safe?
It is only suitable when the action logic is consistent, the anomaly is identifiable and the range is clear.
Why are audit logs needed?
It is used for responsibility tracking, error recovery, security governance, and understanding what the Agent has actually done.
| Related Service | Learn More |
|---|---|
| UI/UX Design Services | View Service Details |
| Project Consultation | Contact JVDS Design Studio |
| Design and Website Development Articles | Read More Related Articles |
 Link copied








